
🎧 Listen to this article: हिंदी · English · தமிழ் · తెలుగు · ಕನ್ನಡ · മലയാളം · ଓଡ଼ିଆ · 日本語 · 中文
🌍 Read this in your language: हिंदी · தமிழ் · తెలుగు · ಕನ್ನಡ · മലയാളം · ଓଡ଼ିଆ · 日本語 · 中文
If your instinct for spotting a scam is "I'd know a fake voice or a badly written email when I see one," a new survey of the people whose job it is to stop these attacks says that instinct is quietly becoming obsolete.
As of today, September 23, 2026, this matters because the survey was conducted recently, between March and May 2026, across 297 senior cybersecurity leaders, mostly Chief Information Security Officers (CISOs) or people in equivalent roles. Its core finding is blunt: AI is making social engineering attacks bigger in volume, more personalized, and more believable, all while making the old warning signs people used to rely on less useful than before. Social engineering, for anyone unfamiliar with the term, just means tricking a person into doing something risky, like handing over a password or approving a payment, rather than breaking into a system through a technical flaw.
What CISOs are actually seeing
The survey asked security leaders about real incidents from the past 12 months, and the numbers show that AI-assisted attacks are no longer a rare, futuristic threat.
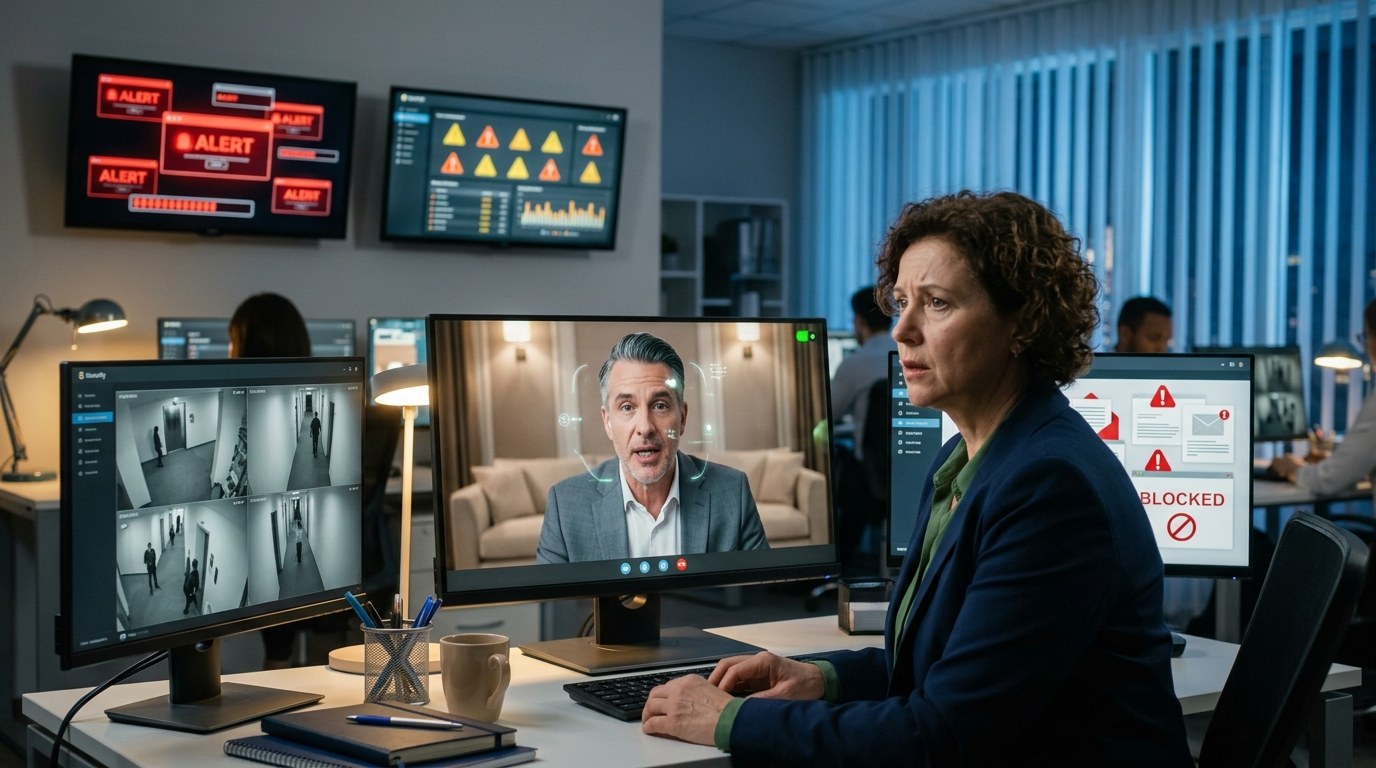
Forty-one percent of CISOs reported at least one social engineering incident involving a deepfake during an employee audio call. A deepfake, in this context, means an AI-generated voice designed to convincingly imitate a real person, such as a company executive asking for an urgent wire transfer. Thirty-six percent reported a similar incident during a video call, meaning attackers are now also faking what people see, not just what they hear.
Traditional attack methods haven't gone away either, and they're still the most common. Seventy-nine percent of respondents reported at least one email-based incident, including phishing (fake emails trying to trick someone into clicking a bad link or handing over information), spear-phishing (the same idea, but personalized to a specific target), or business email compromise, often shortened to BEC, where an attacker impersonates a trusted contact to redirect a payment or request sensitive data. Fifty-eight percent reported at least one incident involving vishing (voice phishing, meaning a scam phone call) or smishing (the same idea over text message).
Put together, these numbers describe a threat landscape where nearly every channel an employee might use to communicate, email, phone, text, video call, has become a potential attack surface, and AI is what's making each of those channels more convincing than before.
Why the old advice is losing its power
Most workplace security training for the last decade has focused on teaching people to "spot the fake": look for typos, watch for a slightly off voice, notice unusual phrasing. The survey's core takeaway is that this approach is running out of road, because AI is specifically good at removing the very flaws people were trained to notice. A cloned voice doesn't sound robotic anymore. A phishing email doesn't have to include broken grammar. The visual and audio cues that used to work as a gut check are becoming less reliable by the month.
That doesn't mean detection is hopeless, but it does mean the response has to shift from "train employees to notice something is fake" toward building verification into the process itself, so that a request doesn't need to be caught as fake in order to be stopped.
What security leaders are being told to do about it
Based on the survey's findings, here's the three-part response being recommended to CISOs and security teams.
Step 1: Turn static training into an adaptive security culture
Rather than teaching employees to visually or audibly "spot the fake," organizations are being encouraged to make secure verification the standard protocol for any high-impact action, regardless of how convincing the request looks or sounds. That means training staff and approvers to pause, verify through a separate trusted channel, and report high-risk requests, whether they arrive by email, phone, video call, a collaboration platform like Slack or Teams, or even through an AI application. Running workforce simulations, essentially practice drills for suspicious AI-related scenarios, is also recommended so organizations can see how employees actually respond before a real incident happens.
Step 2: Harden identity and account recovery against impersonation
Some of the most damaging attacks target the moments when identity is being verified or changed, such as account recovery, privileged access requests, or payment approvals. The recommendation here is to protect those specific workflows with phishing-resistant authentication (login methods that can't simply be phished away with a fake password page), risk-based identity controls, and trusted, pre-established verification channels. Alongside that, organizations are advised to monitor what happens after a successful login or password reset, since a stolen identity is often only valuable to an attacker once it's used for something else.
Step 3: Build detection and response specifically for AI-mediated threats
Finally, the survey recommends connecting the dots between suspicious communications and other high-risk events, such as a new device being registered, a privilege level changing, or an unusual outbound transaction, rather than treating a single strange phone call or email in isolation. Incident response playbooks are also being updated to account for newer risks that didn't exist a few years ago: impersonation across multiple formats at once (audio and video together, for example), AI outputs that have been deliberately manipulated, and AI agents that have been compromised, misused, or allowed to act outside their intended boundaries.
Conclusion
The numbers in this survey describe a straightforward shift: AI hasn't invented social engineering, but it has removed most of the friction that used to make it detectable, and closer to half of surveyed security leaders have already dealt with an AI-assisted impersonation incident in just the past year. The response isn't to train people to have better instincts against something specifically engineered to fool human instincts. It's to build verification into the process so that trust doesn't depend on a gut feeling in the first place.
Merits
- Provides concrete, recent data (297 senior security leaders, a 12-month window) instead of vague warnings about AI-driven fraud.
- Shifts the conversation from "train people better" to "build verification into the process," which is a more durable fix as AI-generated fakes keep improving.
- Covers the full range of channels attackers use, from email to voice to video, rather than focusing on just one format.
Demerits
- Even strong verification processes add friction to legitimate business activity, and some organizations may resist slowing down high-impact approvals.
- Smaller organizations without dedicated security teams may lack the resources to deploy phishing-resistant authentication or post-authentication monitoring at the level described.
- Because the underlying AI technology keeps advancing, today's recommended defenses will likely need continual updates rather than being a one-time fix.
Caution
This article summarizes findings and recommendations from a survey of senior cybersecurity leaders and is intended for general understanding, not as a complete security policy. Organizations should verify current best practices with their own security teams or qualified professionals before implementing any of the measures described here.
Frequently asked questions
- What is a deepfake in this context? — An AI-generated audio or video imitation of a real person, convincing enough to be mistaken for that person during a call.
- What is the difference between phishing and spear-phishing? — Phishing is a general fake message sent to trick recipients into clicking a bad link or sharing information; spear-phishing is the same idea but personalized to target a specific individual.
- What does BEC stand for? — Business email compromise, where an attacker impersonates a trusted contact by email to redirect a payment or request sensitive information.
- What is vishing and smishing? — Vishing is voice phishing carried out over a phone call; smishing is the same kind of scam carried out over text message.
- Why is training people to "spot the fake" becoming less effective? — Because AI-generated voices, videos, and messages increasingly lack the obvious flaws, like typos or robotic-sounding audio, that people were trained to notice.
- What is phishing-resistant authentication? — A login method designed so it can't be bypassed simply by tricking a user into entering their password on a fake page.
- Why should companies monitor activity after a login or password reset? — Because a stolen identity is often only useful to an attacker once it's used to take a further action, so watching for unusual activity afterward can catch abuse that slipped past initial verification.
- What should incident response plans account for now that they may not have before? — Multimodal impersonation (fake audio and video used together), manipulated AI outputs, and AI agents that have been compromised or misused.
Tags
#cybersecurity #aisafety #socialengineering #deepfakes #phishing #ciso #infosec #dataprivacy #businessemailcompromise #identitysecurity
Linux Server Hardening Checklist
30 practical steps to take a fresh Linux box from default to defensible. Enter your email — you'll get the PDF instantly, plus new posts on Linux, security & AI.
Free. No spam — unsubscribe in one click.
Responses
Sign in to leave a response.