
🎧 Listen to this article: English
🌍 Read this in your language: हिंदी · தமிழ் · తెలుగు · ಕನ್ನಡ · മലയാളം · ଓଡ଼ିଆ · 日本語 · 中文
In today's world, AI is becoming a part of many workplace applications, including HR systems. However, simply giving an AI assistant a read-only database connection is not enough. Let's explore why managing permissions is essential in designing an effective HR assistant.
The Importance of Permissions
When someone asks, "Show me this month's payroll," the first question should be, "Who is asking?" Different users have different roles and responsibilities. An employee checking their own payslip, a manager looking at their team's payroll, and an administrator preparing payroll all need access to different data.
If an AI assistant only has a read-only connection to the database, it doesn't automatically ensure that sensitive information is protected. This is where permissions come into play.
Role-Based Access Control (RBAC)
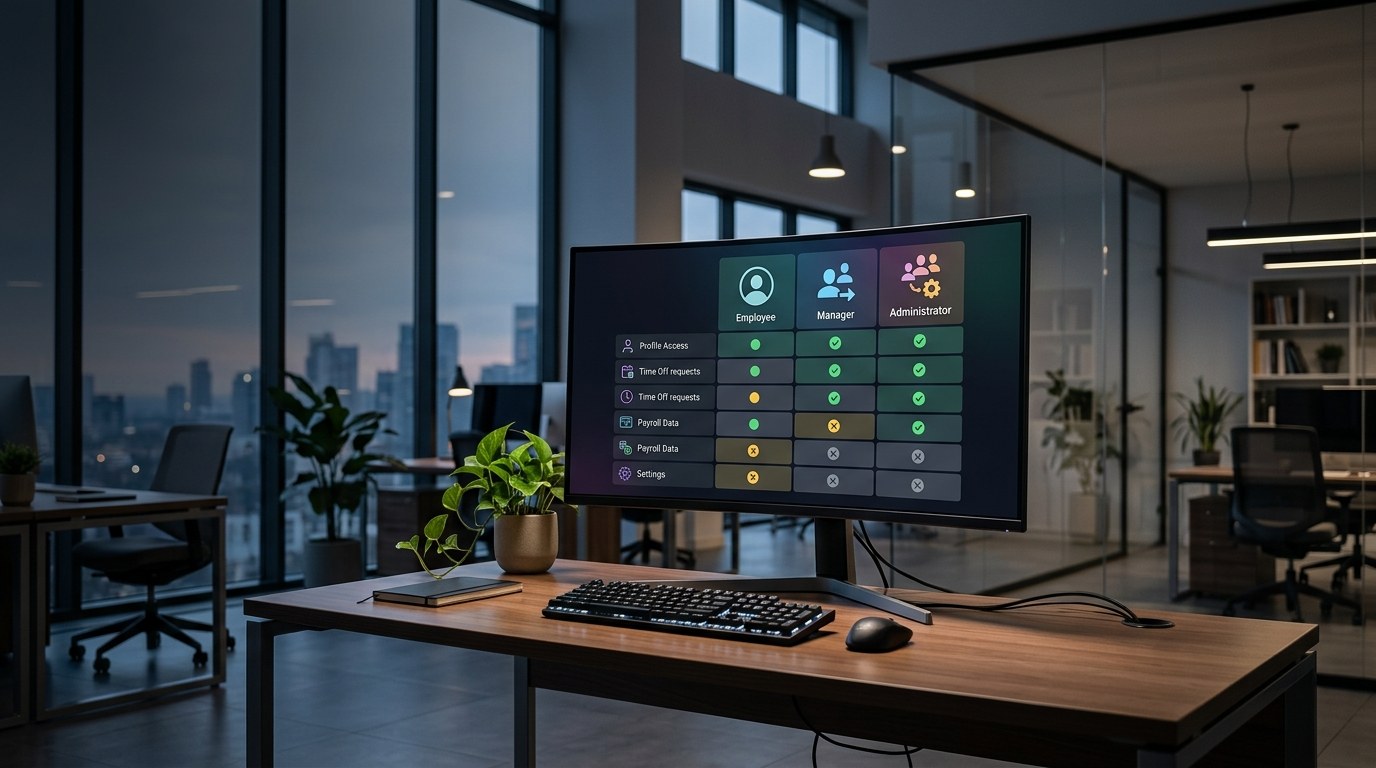
To manage who sees what information, organizations need to implement Role-Based Access Control (RBAC). This means creating a role and permission matrix that defines what data each user can access based on their role. For example:
- An employee can view only their own payslip.
- A manager can see payroll information for their team.
- An administrator can access all payroll data.
Granular Permission Checks
It's not enough to just check if a query is read-only. Permission checks need to consider both the type of operation and the specific data being requested. For instance:
- If an employee asks for their payslip, the system should ensure they only see their own data.
- If a manager requests information about leave, the results should only reflect their team's requests.
A read-only query layer can limit what can be changed, but it doesn't control which rows or columns a person can see. Even aggregate data can reveal sensitive information if not handled correctly.
Integrating AI into HR Workflows
An AI assistant should be integrated into existing HR workflows to ensure that data remains accurate and compliant. For instance, payroll processing involves various elements like contracts, attendance, and approved leave. The assistant should query this information while respecting the established permissions.
WorkBento, a self-hosted Python HR and workplace platform, offers an example of how to implement these concepts. It uses a guarded, read-only SQL layer with permission-aware access to enforce data access policies. This means the assistant can provide information while still maintaining the necessary boundaries.
Self-Hosting Considerations
If you choose to self-host an HR application, there are additional responsibilities to consider. This includes:
- Conducting access reviews to ensure only the right people have access to sensitive information.
- Setting up backup restoration processes to recover data if needed.
- Regularly upgrading the system to maintain security and functionality.
When deploying an AI assistant, organizations must also think about what data the AI model provider receives and how it will be used.
Testing Permissions
Before rolling out an AI assistant, it's crucial to test how it handles various requests. Here are some scenarios to check:
- Employee asks for a payslip: Ensure they only access their own data.
- Manager asks about leave: Verify results respect the manager's team scope.
- User names a different workspace: Confirm the request cannot cross workspace boundaries.
- Prompt asks to update a salary: The assistant should not be able to perform this change.
- User asks for hidden fields: Responses must not bypass the application's permission policy.
Conclusion
Designing an HR assistant involves more than just connecting to a database. It requires careful consideration of permissions and roles to ensure data security and compliance. By implementing robust access controls and integrating AI into existing workflows, organizations can create a more effective and secure HR system.
Merits
- Enhanced data security through role-based access.
- Improved compliance with organizational policies.
- Streamlined HR processes with AI assistance.
Demerits
- Complexity in setting up and managing permissions.
- Potential for errors if permissions are not correctly configured.
- Ongoing responsibility for self-hosted solutions.
Caution
This article is meant for educational purposes. Any placeholder values in examples must be replaced with actual data. Readers should verify claims against the original source before relying on them.
Frequently asked questions
- What is Role-Based Access Control (RBAC)? — RBAC is a method of restricting system access to authorized users based on their roles within an organization.
- Why is read-only access insufficient for HR applications? — Read-only access does not prevent users from seeing sensitive information they shouldn't have access to, based on their roles.
- How can AI be integrated into HR workflows? — AI can assist in querying information while adhering to existing permission structures and workflows.
- What should organizations consider when self-hosting HR applications? — Organizations must manage access reviews, backups, upgrades, and monitor operations to ensure security and compliance.
- How can I test the permissions of an AI assistant? — Testing can involve simulating requests from different roles to verify that access controls are functioning correctly.
- What is the importance of a role and permission matrix? — It defines what data each user can access based on their job responsibilities, ensuring security and compliance.
Tags
#hr #permissions #ai #workbento #software #self-hosting #data-security #role-based-access #automation #workplace
Incident Response: First Hour
A calm, evidence-preserving checklist for establishing control, bounding impact, communicating clearly, and containing an incident safely.
Free. No spam — unsubscribe in one click.
Responses
Sign in to leave a response.